 BUSINESS

OpenAI Daybreak is OpenAI’s cybersecurity program that lets defenders scan software for vulnerabilities with AI; OpenAI said on November 17 that NATO works with it too, and national cyber agencies in Germany, France and Poland already have access. In an EU review, 95% of 88 assessed findings were genuine issues, confirmed by humans.
Key facts
- According to OpenAI’s November 17, 2026 announcement, NATO’s NCIA has access to Daybreak; NATO has used up to 300 billion tokens a month.
- ENISA, France’s ANSSI and national cyber agencies in Germany and Poland already have access to OpenAI’s cyber models.
- In an ENISA and CERT-EU review of 27 software projects, 95% of 88 issues assessed by maintainers were confirmed as genuine.
Researched and written with AI, to Luigi's brief, positions and editorial rules. Automatically checked against the sources. How I work →
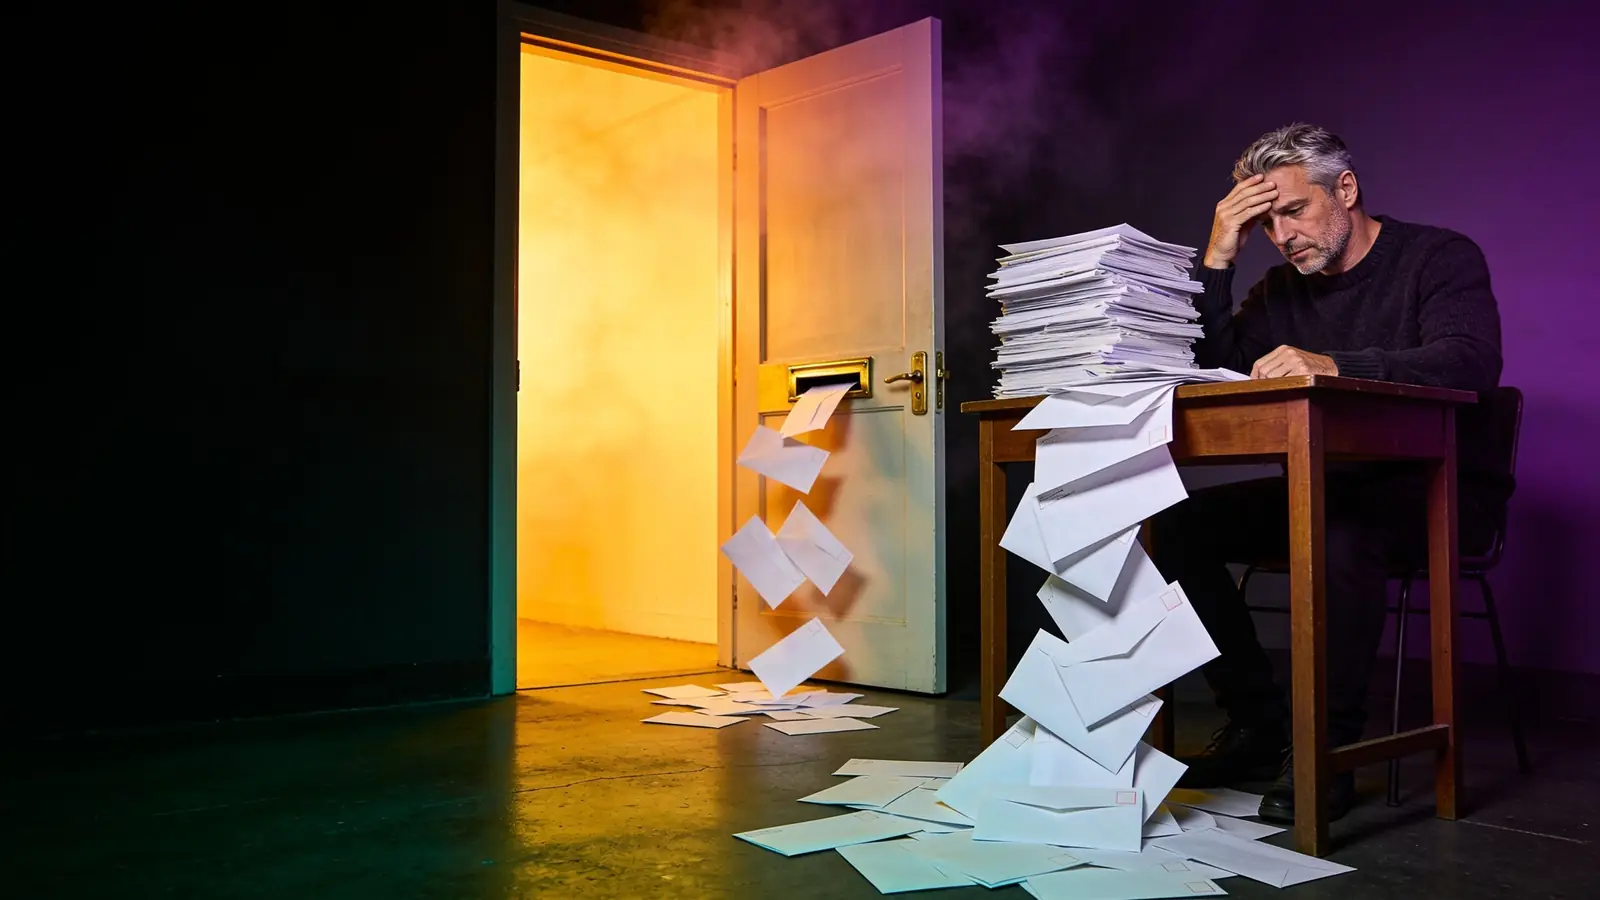
Picture a pile of letters on your desk every morning. Each one says: “Here is a vulnerability in your software.” Ninety-five out of a hundred are right. Sounds like a gift. It is. But only for whoever reads the letters and closes the holes.
That is the world OpenAI just made a little bigger with Daybreak.
What is OpenAI Daybreak?
Daybreak is OpenAI’s cybersecurity program: security teams use OpenAI’s models to review software, investigate suspicious activity, validate vulnerabilities and build and test fixes. According to OpenAI’s announcement of November 17, OpenAI provides the Alliance’s core institutions with cyber models through NATO’s NCIA. OpenAI says NATO has used up to 300 billion tokens a month in this work. The EU cyber agency ENISA and national cyber agencies in France (ANSSI), Germany and Poland already have access. OpenAI does not say which German agency.
The results OpenAI cites:
- ENISA used the models to find four vulnerabilities in software used across EU institutions. All four have fixes.
- A joint ENISA and CERT-EU report reviewed 27 software projects. Of 88 potential issues assessed by maintainers, 95% were confirmed as genuine.
- CERT Polska found six vulnerabilities in MikroTik RouterOS, which MikroTik has since fixed.
Finding is no longer the bottleneck
Here is what I find interesting: the 95% is not the machine’s score alone. It is measured against what maintainers checked. Humans looked at every finding, tested it, signed it off. Human in the loop is not a fig leaf here. It is the part of the job that is left.
That changes the math. Yesterday I wrote about Google’s report that attacker AI turns patches into exploits. Today defenders get the same speed. Both sides find faster. Who wins gets decided afterwards: at the patch.
To me this is the oldest rule of AI adoption: it does not fix broken ways of working, it widens the cracks. A team with clear ownership gets a tool that makes it faster. A team where nobody owns the WordPress plugin on the campaign microsite gets a bigger pile of letters.
The catch for companies
Daybreak is not a subscription you just buy. Organizations and individuals apply, and OpenAI vets applicants and their intended use first. There are two tiers: Daybreak Blue for defense (finding, validating and fixing vulnerabilities) and Daybreak Red for authorized penetration testing. OpenAI lists no prices on the page. For utilities, local governments, nonprofits and open-source projects, OpenAI has pledged $1 billion in subsidized access.
One line from NCIA general manager Dylan Browne stands out: NATO wants to understand token consumption and costs so it can evaluate competing solutions. So even NATO buys AI like electricity. Meter it, compare it, keep the option to switch.
What I would do now
- An owner list for the marketing stack: every microsite, plugin and tracking script with a name next to it. Who gets the letter when a vulnerability is reported? (The Optimizely case shows why.)
- Ask your agency and IT: do you run AI reviews like Daybreak or Codex Security, and how fast do you ship fixes? A patch deadline belongs in the contract; see Anthropic’s 30-day rule.
- If you build software: apply for Daybreak Blue, but decide first who reviews and signs off the findings.
Bottom lineOnce AI can find every hole, knowledge is no longer scarce. The hand that ships the fix is.
Got AI news? Submit news →
FAQ
What is OpenAI Daybreak?
OpenAI’s cybersecurity program: security teams use OpenAI models to review software, validate vulnerabilities and build fixes. Daybreak Blue covers defense, Daybreak Red authorized penetration testing.
Can companies use Daybreak?
Organizations and individuals can apply; OpenAI vets applicants and their intended use before granting access. OpenAI lists no prices on the Daybreak page.
Does Germany use Daybreak?
According to OpenAI, national cyber agencies in Germany, France (ANSSI) and Poland already have access to its cyber models. OpenAI does not name the German agency.
Source
OpenAI: Strengthening NATO and allied cyber defenses with AI
More sources
- OpenAI – Zugang, Blue/Red, Frontline Defenders 1 Mrd. US-Dollar, Stand 17.11.2026
- The Decoder
 DealHootsuite's sale: the 50% ends a week before Black Friday
 NewsProton Lumo Desktop: sold as private, auto-approve by default
 NewsHeyGen Avatar 6: your twin posts the video you never dared to post
